
Why Your AI Agent Is a Loaded Weapon Without a Safety
It's 3 AM. Your agent has Gmail, Notion, and GitHub access. It runs a batch job and sends 47 unapproved emails to your entire client list.
You wake up to a inbox full of apologies you didn't write. That's the moment most builders learn that one wrong write costs more trust than 100 correct reads ever build. And there's a specific architectural pattern that stops this cold, one that most tutorials skip entirely. I'll show you exactly what it is after we cover the foundation.
The "move fast" automation mindset treats every agent action as equally safe. It isn't. Reading your inbox is harmless. Sending an email is not. Deleting a Notion database is not. Pushing to main is not.
Here's where it gets interesting: the protocols everyone is racing to adopt don't fix this. Not by themselves.
What Is the Approval Gate Pattern (And Why Most Tutorials Skip It)
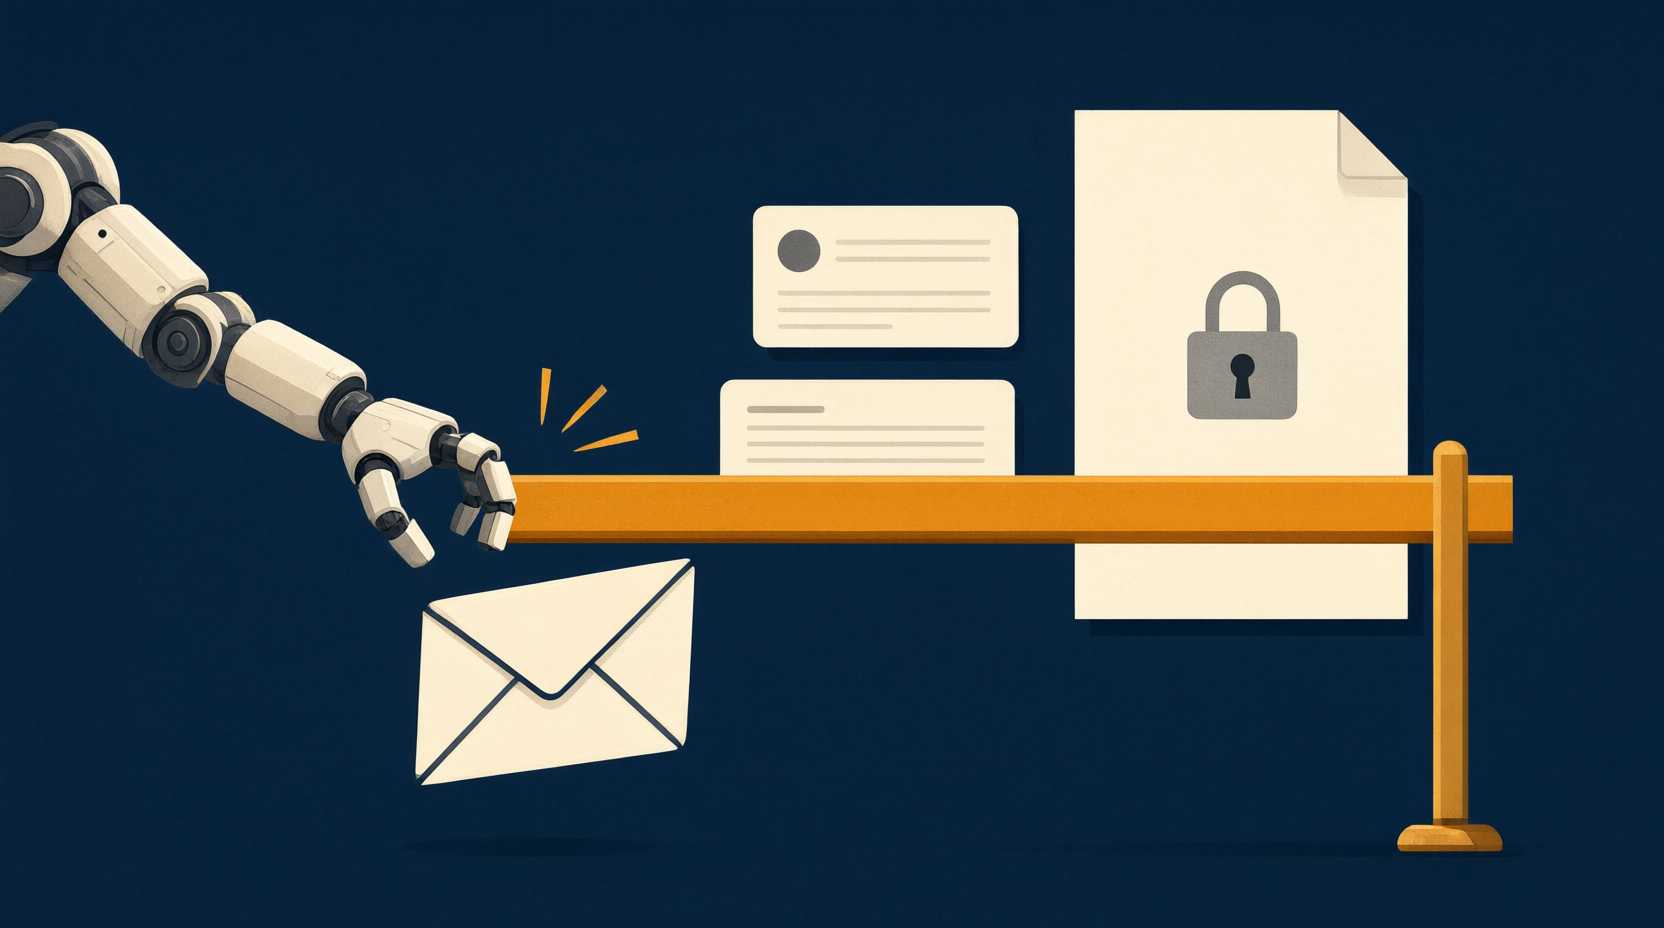
The approval gate pattern intercepts consequential actions (writes, sends, deletes, payments) and requires human or policy approval before execution. Simple in concept. Rare in practice.
Map your agent's actions into three tiers:
- Read-only (auto): fetching emails, listing Notion pages, reading GitHub issues. Zero risk. Let it run.
- Reversible writes (batch approve): creating drafts, adding Trello cards, opening issues. Low blast radius. Review in groups.
- Irreversible (hard gate): sending email, deleting records, merging PRs, moving money. One mistake, permanent damage.
Now for the part nobody talks about: MCP and A2A alone don't solve this. As of September 2026, the Agentic AI Foundation (AAIF) governs both protocols, with MCP handling agent-to-tool connectivity and A2A handling agent-to-agent communication. But protocols standardize connectivity, not consequence.
Connecting an agent to Gmail is a five-minute problem. Deciding what that agent is allowed to do with Gmail is the problem that keeps you up at night.
Here's how this maps directly onto the July 2026 MCP spec and A2A v1.0.
How to Wire Approval Gates Into MCP and A2A Without Breaking Flow
MCP's July 28, 2026 specification moved to a stateless design, dropping session identifiers in favor of request-level metadata. That's your opening.
Tag every tool call with a risk level and required approver. A middleware function intercepts the call, checks the tag, and routes high-risk actions to a queue instead of executing them.
async function gatedToolCall(toolName, params, meta) { const risk = classifyRisk(toolName); // "read" | "reversible" | "irreversible" if (risk === "irreversible" && !meta.approvedBy) { return enqueueForApproval({ toolName, params, requestedBy: meta.agentId }); } return executeTool(toolName, params); }
On the A2A side, signed Agent Cards let you declare which agents may request which actions from which peers. A research agent can read your Notion workspace. It cannot ask your publishing agent to send anything.
But that's only half the picture. Neither protocol natively provides tamper-evident event logging. Enterprises are advised to run a gateway layer for observability and audit trails, and that advice is worth taking seriously.
Next, let's connect this to Gmail, Notion, Trello, and GitHub in one flow.
The 15-Minute Setup: Connecting Gmail, Notion, Trello, and GitHub With Gates On
OAuth each service once, then define the policy per action:
- read_inbox = auto
- create_draft = batch approve
- send_email = hard gate
- create_github_issue = batch approve
- merge_pull_request = hard gate
Use n8n or an MCP connector layer to build the workflow, then insert an approval node before every write action. Route all approvals to a single inbox: Slack, Telegram, or email. Context-switching across four dashboards is how gates get bypassed.
This is where most people get stuck: they enable auto-execution on day one. Don't. Run a dry-run mode for 48 hours. Let the agent propose actions and log what it would have done. Review the log. You'll be surprised how often the agent's judgment differs from yours.
The final piece: scaling this across a team without becoming the bottleneck.
From Solo Builder to Team: Scaling Approval Gates Without Slowing Down
Role-based gates are the answer. Junior or newly deployed agents get stricter policies. Agents with a clean track record earn auto-approve on reversible actions.
Batch approvals matter more than you'd think. Grouping low-risk writes into a single review beats 40 individual pings that train your team to click "approve" without reading.
Treat the audit trail as a feature, not overhead. Gate logs prove compliance, and they're your best debugging tool when an agent behaves unexpectedly.
And apply the 80/20 rule ruthlessly: gate the 20% of actions that cause 80% of damage. Auto-run everything else.
Your Next Move: Ship the Gate Before You Ship the Agent
Write a one-page approval policy today. List every action your agent can take. Mark each one auto, gate, or forbidden. That single page prevents the 3 AM nightmare.
Track three metrics: approval latency, gate bypass rate, and incident count. Your target on that last one is zero irreversible mistakes.
"We'll add gates later" is the most expensive sentence in agent development. Later is exactly when the 47 emails go out.
The core takeaway: connectivity is cheap, consequence is expensive, and the gate belongs between them.
Your next action, in the next 10 minutes: open your agent stack, find one irreversible action, and gate it before you sleep tonight.
Which tier is your agent currently operating without gates? Read, reversible, or irreversible? The tradeoffs are real, and I'd genuinely like to hear how you're handling it. Drop your setup below.